
Inquire Now
Key Strategic Points
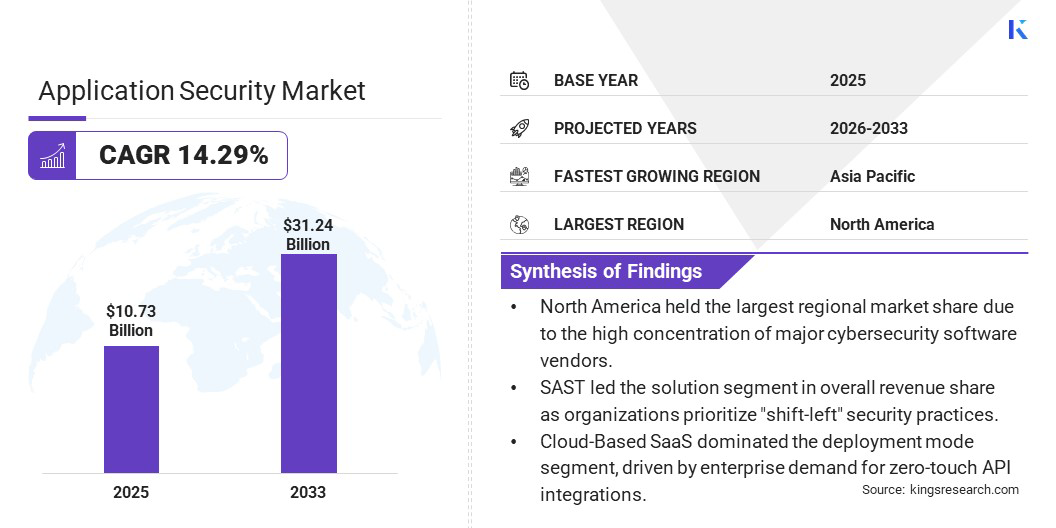
According to Kings Research, the global application security market size was valued at USD 10.73 billion in 2025 and is projected to reach USD 31.24 billion by 2033, exhibiting a CAGR of 14.29% during the forecast period.
The market is growing as cyber threats rise, cloud-based applications become increasingly used, and regulatory compliance becomes necessary. Organizations are adopting AI-based security solutions, shifting to DevSecOps practices, and investing in mobile and web application security.
The market is being driven by organizations' focus on solid security frameworks to protect applications in the face of evolving cyber risks and regulatory mandates.
Major companies operating in the market are IBM Corporation, Qualys, Inc., Veracode, Hewlett Packard Enterprise Development LP, Rapid7, HCL Technologies Limited, Snyk Limited, LevelBlue, Black Duck Software, Inc., Checkmarx Ltd., Open Text Corporation, Broadcom, Thales, and Oracle.
The market is driven by increasing awareness of cybersecurity risks. Governments are aware of how costly data breaches can be, both financially and in terms of reputation, and are investing more in security infrastructure.
Enterprises are prioritizing security spending to protect applications from cyberattacks and to ensure regulatory compliance. Security budgets are expanding across industries, with organizations adopting proactive threat management solutions. For instance, in January 2024, India's government launched the National Cybersecurity Reference Framework (NCRF), a strategic guideline aimed at harmonizing cybersecurity practices across the country. The framework is sector-specific and addresses critical sectors such as telecom, power, transportation, finance, strategic entities, government agencies, and healthcare, and provides guidance for enhancing cybersecurity infrastructure. The framework also recommends that organizations set aside at least 10 percent of their overall IT budget for cybersecurity, with support from senior management or the board of directors, to ensure it is successfully implemented.
Advanced security tools, including zero-trust architecture and runtime application self-protection (RASP), are gaining traction as organizations strengthen security frameworks to enhance business resilience and ensure long-term sustainability. The demand for comprehensive application security solutions continues to grow, driven by the need for enhanced cybersecurity strategies.
The increasing frequency of cyberattacks is driving the application security market. Businesses across industries face a growing number of security threats, including ransomware, SQL injection, and cross-site scripting.
Attackers exploit vulnerabilities in applications to gain unauthorized access, steal sensitive data, and disrupt operations. Organizations are prioritizing investment in application security solutions to mitigate financial losses and reputational damage. According to a 2024 study by the National University, cloud environment intrusions rose 75% compared to the previous year. In 2023, ransomware attacks affected over 72% of businesses globally. Cloud-based data was involved in 82% of data breaches, making ransomware the dominant threat. Additionally, 52% of organizations experienced ransomware incidents that severely disrupted their business systems and operations.
The demand for advanced security tools, such as web application firewalls, runtime protection, and automated threat detection, is increasing. Strengthening security frameworks has become a strategic priority, accelerating the adoption of application security solutions across enterprises.
Integrating application security solutions within existing IT infrastructures poses a significant challenge to industry growth. This results in compatibility issues for organizations, increases deployment costs, and requires specialized knowledge.
Companies are turning to automated security testing, AI-driven threat detection, and cloud-native security solutions that simplify deployment. Organizations are also embracing DevSecOps models, integrating security into the software development lifecycle to avoid disruptions.
Organizations are also utilizing managed security services and security-as-a-service (SECaaS) models to improve protection and reduce the strain on internal IT departments.
The growing emphasis on secure software development practices is driving growth in the application security market. Organizations are integrating security throughout the software development lifecycle (SDLC) through DevSecOps practices.
Embedding security controls at each development stage enhances application resilience against cyber threats. Security testing tools such as static application security testing (SAST) and dynamic application security testing (DAST) enable developers to identify vulnerabilities early.
Automated security testing reduces remediation costs and strengthens application security. Businesses are prioritizing DevSecOps frameworks to align security with agile development processes.
| Segmentation | Details |
| By Component | Solution, Services (Managed, Professional) |
| By Deployment | Cloud-based, On-premises |
| By Organization | Small and Medium Enterprises, Large Enterprises |
| By Security Testing | Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), Interactive Application Security Testing (IAST), Run-Time Application Self Protection (RASP) |
| By Industry Vertical | IT & Telecommunications, BFSI, Healthcare, Government, Retail & e-commerce, Manufacturing, Others |
| By Region | North America: U.S., Canada, Mexico |
| Europe: France, UK, Spain, Germany, Italy, Russia, Rest of Europe | |
| Asia Pacific: China, Japan, India, Australia, ASEAN, South Korea, Rest of Asia Pacific | |
| Middle East & Africa: Turkey, UAE, Saudi Arabia, South Africa, Rest of Middle East & Africa | |
| South & Central America: Brazil, Argentina, Rest of South & Central America |
Based on region, the market has been classified into North America, Europe, Asia Pacific, Middle East & Africa, and South & Central America.
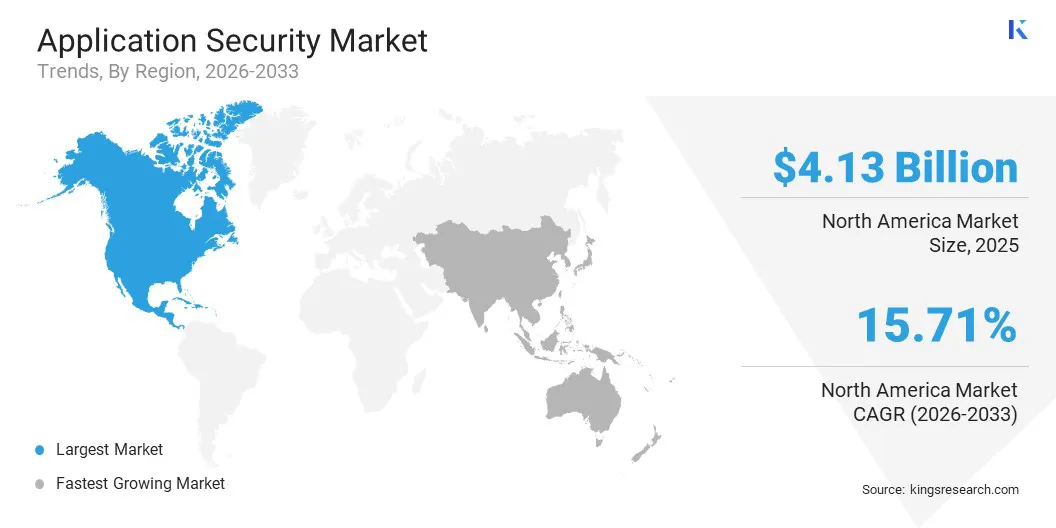
North America accounted for the largest share of the application security market in 2025. In North America, the increasing frequency and sophistication of cyberattacks, such as ransomware and data breaches, are driving the market.
High-profile breaches across industries, including finance, healthcare, and retail, have exposed vulnerabilities in applications, making security a critical priority. The need to protect sensitive customer data, intellectual property, and financial assets has led to a surge in demand for advanced security solutions.
Companies are increasingly investing in application security tools to prevent unauthorized access and minimize the risk of cyberattacks. The FBI’s Internet Crime Report 2024 indicates that the public filed 859,532 cybercrime complaints, while reported losses exceeded USD 16 billion, reflecting a 33% increase from 2023. Investment fraud involving cryptocurrency accounted for the highest losses, exceeding USD 6.5 billion. California, Texas, and Florida reported the highest number of cybercrime complaints.
Additionally, North American organizations are subject to strict data protection laws like the General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA), requiring organizations to implement strong cybersecurity practices to protect sensitive data. These regulations have prompted more investment in application security to comply with them and avoid hefty penalties.
The market in Asia Pacific is also poised for growth over the forecast period. According to Kings Research, the accelerating pace of digital transformation across industries in Asia Pacific is a key factor driving the application security industry.
Businesses are increasingly adopting digital technologies, including cloud computing, IoT, and mobile applications, to enhance operational efficiency and customer engagement. According to the Asian Development Bank’s 2025 report, South Asian countries are increasingly developing Digital Public Infrastructure (DPI), including digital identity, interoperable payments, and data exchange platforms, to support digital economies and improve access to public services. The region is leveraging DPI across sectors such as healthcare, education, agriculture, transport, and logistics, creating opportunities for greater digital inclusion, economic growth, and more efficient service delivery.
As these digital ecosystems expand, so does the attack surface, creating new vulnerabilities. Organizations are investing in advanced application security solutions to safeguard sensitive data, maintain customer trust, and ensure business continuity amid the growing digitalization of services across industries such as finance, healthcare, and manufacturing.
The application security industry is characterized by a large number of participants, including both established corporations and rising organizations. Major market participants are focusing on securing funding and making strategic investments to strengthen the resilience of critical infrastructure sectors such as finance, healthcare, and energy.
Many firms are receiving funding from both government agencies and private investors to develop advanced security technologies, such as AI-driven security solutions and blockchain-based systems, which help protect against evolving cyber threats. These investments are accelerating the development of cutting-edge security solutions and enabling companies to scale their operations.
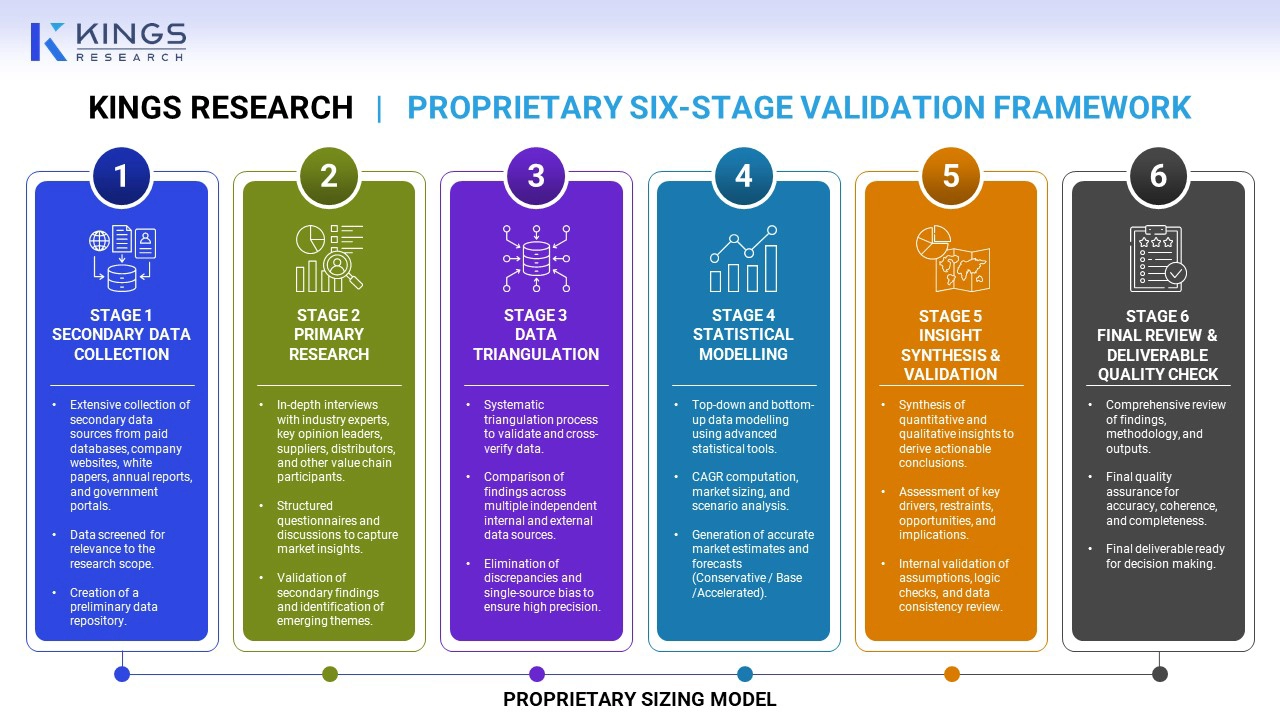
How We Gather This Information
Our methodology triangulates insights from multiple independent and publicly available research databases and is further validated against regulatory filings and public company disclosures. All estimates are cross-verified; no single-source data is presented without validation.
Frequently Asked Questions

Sunanda is a proficient research analyst with strong cross-domain expertise, excelling in identifying market trends and delivering insightful analyses across various industries, including consumer goods, food & beverages, healthcare, and more. Her ability to connect insights from diverse sectors enables her to offer actionable recommendations that support strategic decision-making in a range of business contexts. Sunanda's research is driven by thorough data analysis and her commitment to providing relevant, data-driven insights. Her keen eye for patterns allows her to spot emerging opportunities before they become mainstream. Sunanda's synthesis of cross-sector learnings often reveals unconventional solutions that clients find invaluable. She adapts her analytical frameworks to suit each industry's unique nuances, ensuring reports are both accurate and contextually relevant. Clients appreciate her ability to deliver crisp, actionable findings under tight deadlines, consistently exceeding expectations with her thoroughness and insight.
Habi is a seasoned research and consulting leader with renowned experience in guiding clients on strategic growth and transformation initiatives across global markets. He has led high-performing research teams that deliver actionable insights on market expansion, M&A strategies, opportunity assessment, new business development, and product launches. His project portfolio spans large petrochemical producers, electronic device manufacturers, lubricants companies, and other leading enterprises across diverse industrial and consumer sectors. He currently heads the research department at Kings Research, where he is responsible for setting the research agenda, mentoring analysts, and ensuring client-ready deliverables that support executive decision-making. With extensive experience in market intelligence, strategic research, and consulting, Habi brings a strong understanding of evolving industry dynamics, competitive landscapes, emerging opportunities, and business growth challenges. His expertise includes developing research frameworks, translating complex market data into actionable strategic recommendations, and working closely with senior stakeholders to address critical business questions. He has also contributed to building research capabilities, strengthening analytical methodologies, and driving a culture of quality and insight-led decision-making within research teams. His cross-industry exposure enables him to connect market trends with broader business implications and provide perspectives that help organizations identify opportunities, mitigate risks, and make informed strategic decisions.


